Amazon Patches Critical AWS Bedrock Security Flaws
Amazon patched critical AWS Bedrock AgentCore security flaws that could have exposed internal data and cloud credentials.
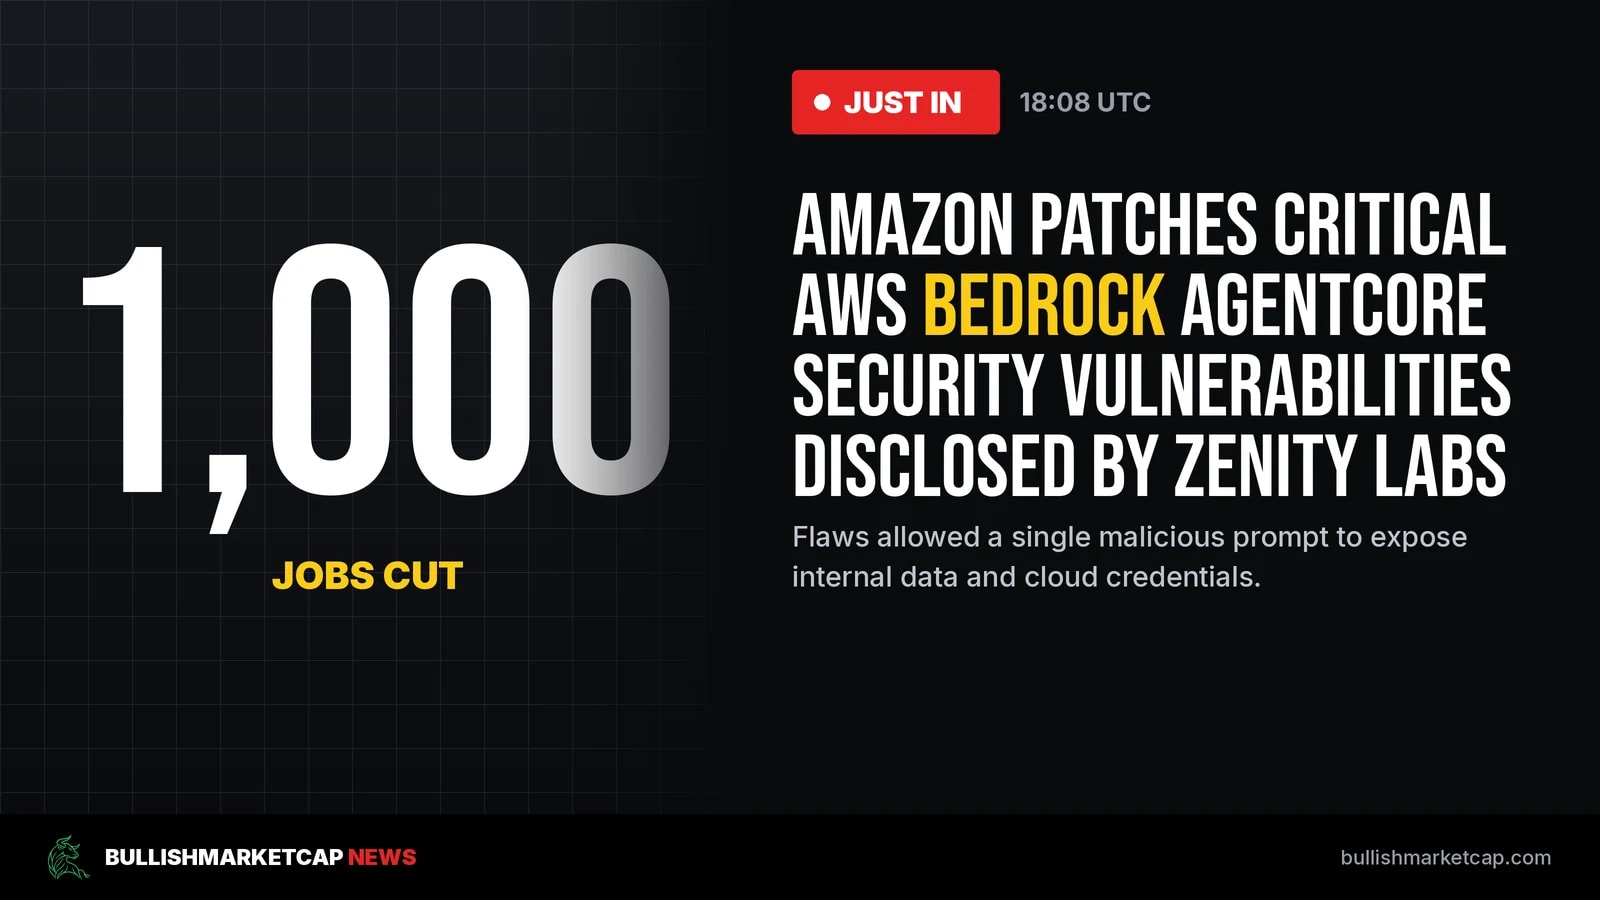
Amazon.com faces scrutiny following the disclosure of critical AWS Bedrock AgentCore security flaws by Zenity Labs, which affected all agents within an account. According to YahooStocks5, researchers determined that a single malicious prompt could expose internal data and cloud credentials prior to mitigation by AWS.
Security Exposure and AI Strategy
Instant Telegram notifications for large on-chain moves.
The Bedrock AgentCore vulnerabilities highlight primary risks associated with artificial intelligence integration. Heavy infrastructure capital expenditures rely on enterprise trust in cloud security tools to protect data and credentials. The security issues surfaced alongside workforce adjustments that included nearly 1,000 job cuts across core units while hiring continued for artificial intelligence focused roles.
Enterprise Monitoring and Compliance
Market participants are tracking how security incident disclosures and enterprise adoption metrics evolve over subsequent quarters. Analysts note that monitoring customer churn and compliance costs tied to security infrastructure provides insight into whether high capital spending on artificial intelligence translates into long-duration contracts.
Key facts
- Zenity Labs disclosed critical AWS Bedrock AgentCore security flaws affecting all account agents.
- A single malicious prompt could expose internal data and cloud credentials before AWS mitigation.
- Amazon cut nearly 1,000 jobs across core units while continuing AI-focused hiring.
Source: finance.yahoo.com
This article is for information only and is not investment advice. BullishMarketCap news is produced with AI assistance from public sources and reviewed by our editors; see our editorial policy. Spotted an error? Tell us.