Near AI Breach Exposes User Data and AI Agent Logs
An attacker exploited an SGLang vulnerability to access internal NEAR AI systems, exposing account records and legacy agent data.
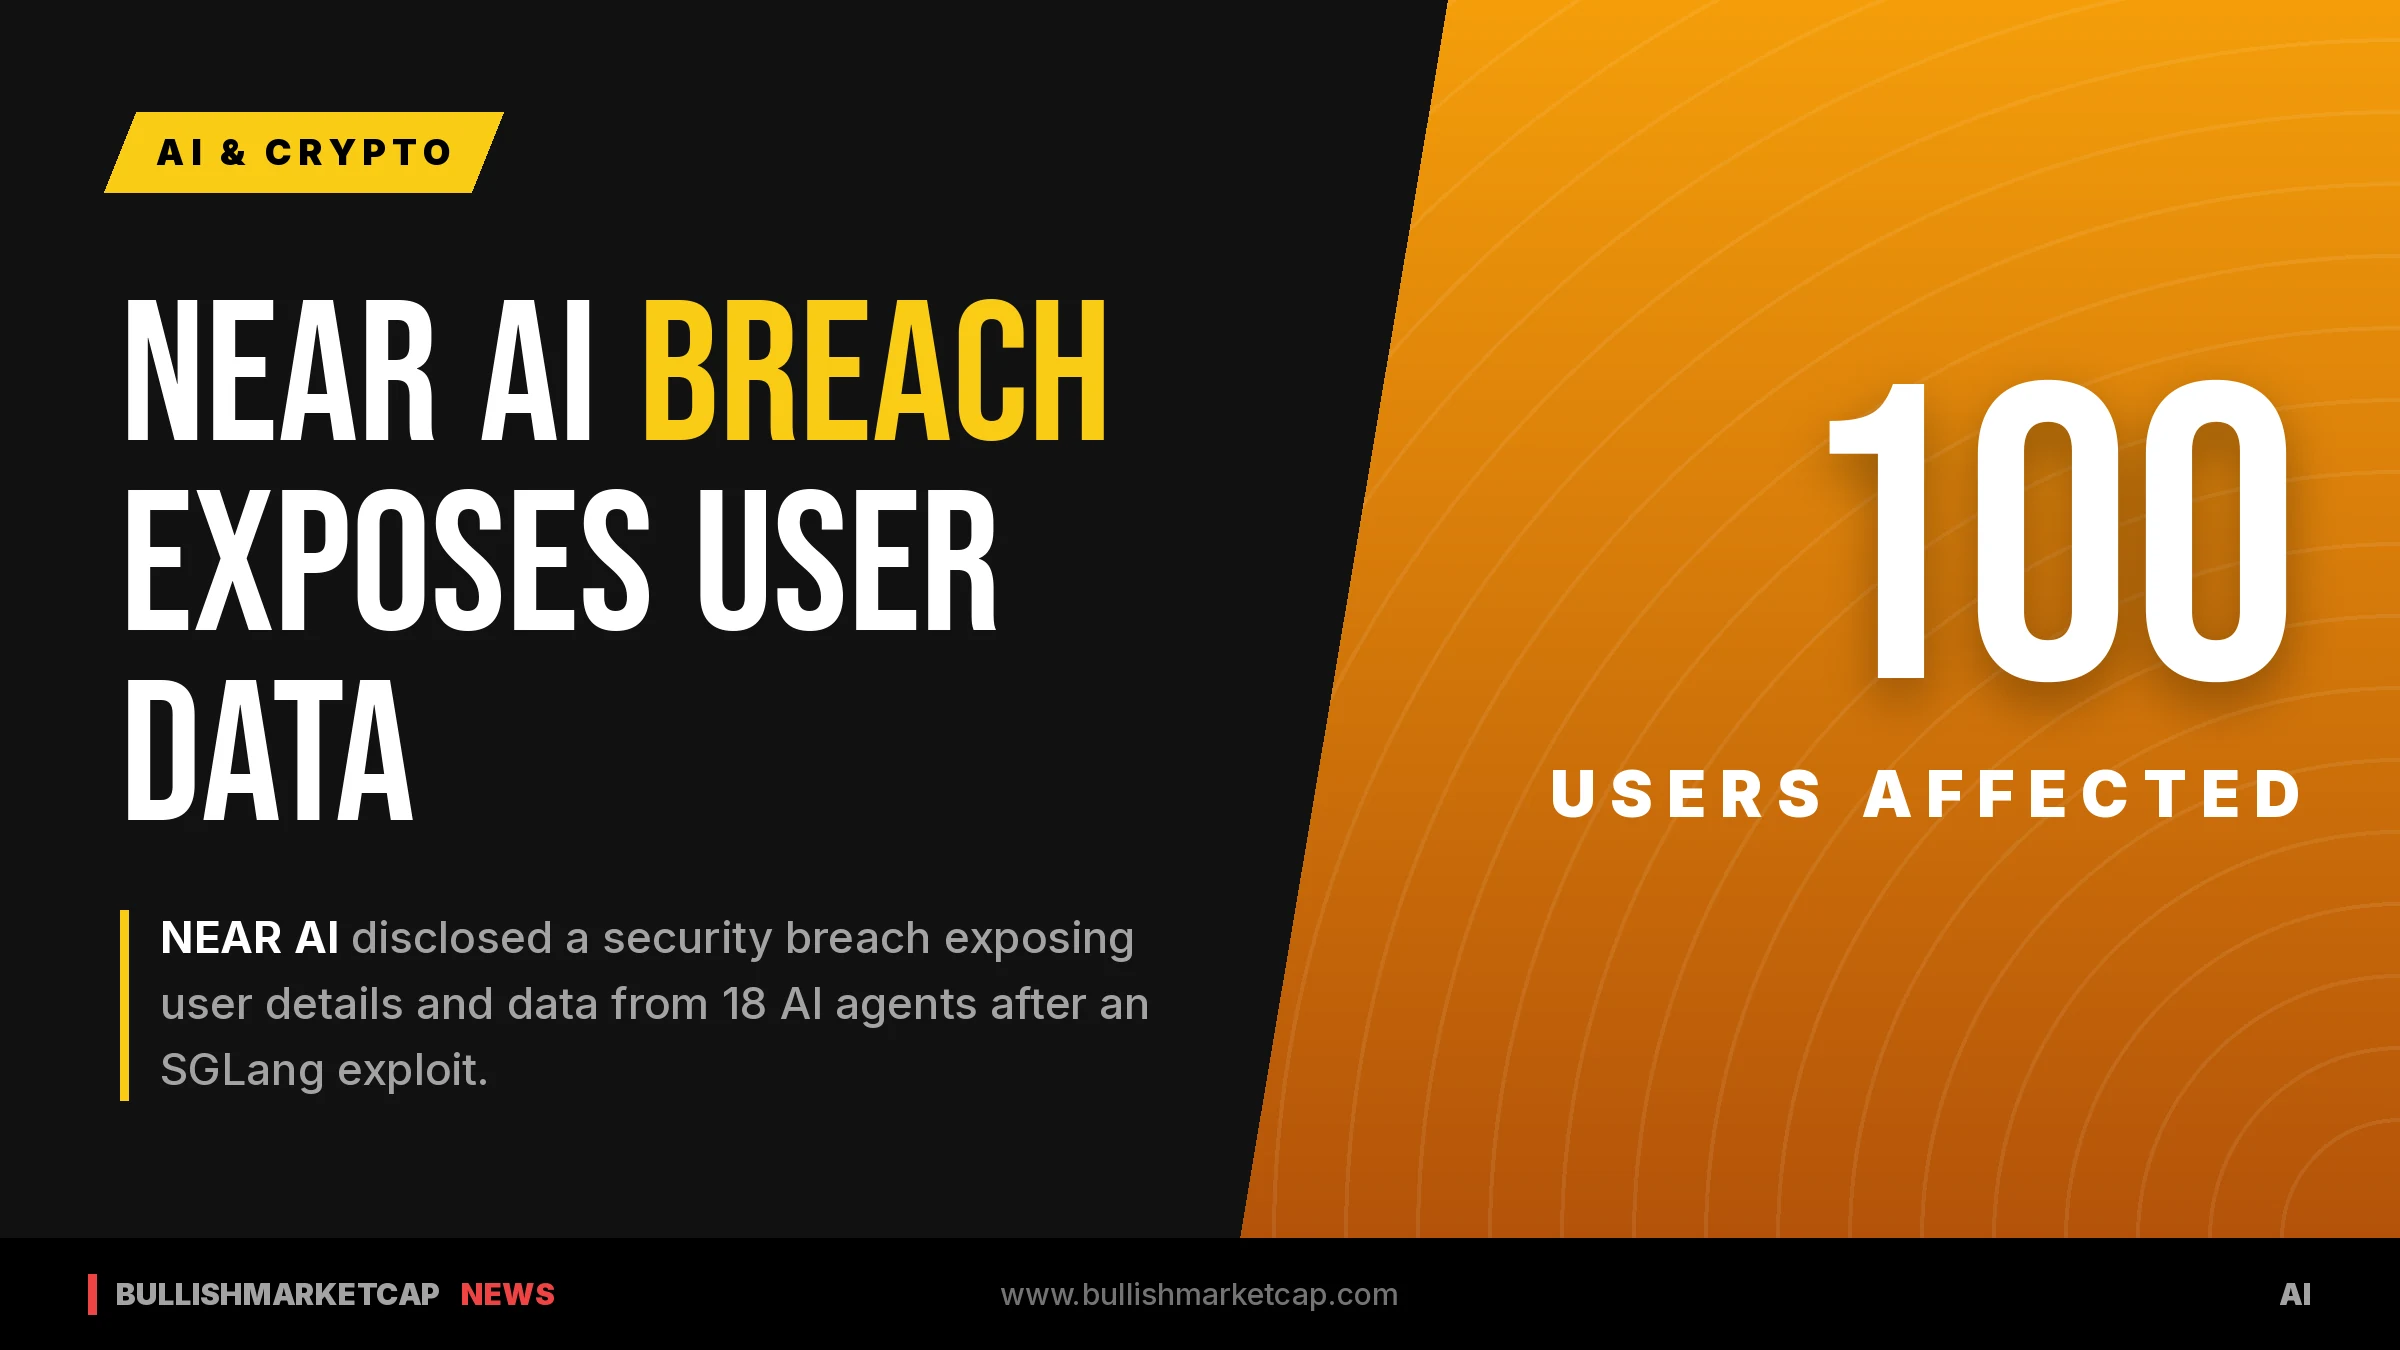
NEAR AI disclosed a security breach in which an attacker exploited a remote code execution vulnerability in SGLang, an open-source engine used to run AI models. According to the company's November 9 report, the intrusion allowed the attacker to execute commands on an inference server and breach other parts of the infrastructure.
Investigators traced the activity to an internal system linked to Private Chat, a retired feature. The attacker downloaded names and email addresses belonging to approximately 100 users, alongside subscription plan and account balance information for some. Additionally, data from 18 older AI agents on an older deployment was accessed, exposing chat histories, settings, and logs. These particular agents were not operating within NEAR AI's confidential computing environment.
Instant Telegram notifications for large on-chain moves.
Credentials and Cloud Exposure
The breach also exposed NEAR AI Cloud API keys belonging to two customers. The company stated that both keys have been revoked, though it did not specify whether the attacker utilized them. Confidential-mode requests processed on November 8 may have been visible during the incident, but the investigation found no evidence that stored Private Chat conversations or uploaded files were accessed.
Hardware-backed privacy protections, such as trusted execution environments, failed to prevent the software-level vulnerability. NEAR AI acknowledged that hardware isolation does not protect against vulnerabilities in software running inside the protected environment.
Mitigation and Response
Upon detecting the breach, NEAR AI revoked active sessions and administrative credentials, replaced agent tokens, took Private Chat offline, and deployed a fix for the SGLang vulnerability across inference servers. The project also reported the vulnerability to SGLang developers.
Key facts
- An attacker exploited an SGLang software vulnerability to breach NEAR AI internal systems.
- Account details for approximately 100 users and data from 18 older AI agents were exposed.
- Two customer Cloud API keys were exposed and subsequently revoked.
- NEAR AI deployed a fix across all inference servers and revoked active sessions.
Source: decrypt.co
This article is for information only and is not investment advice. BullishMarketCap news is produced with AI assistance from public sources and reviewed by our editors; see our editorial policy. Spotted an error? Tell us.