Keystone Destroys 18,835 Wallets After Key Breach
Hardware wallet maker Keystone will destroy 18,835 devices and suspend shipments after hackers stole an authentication key and exposed 25,964 customer records.
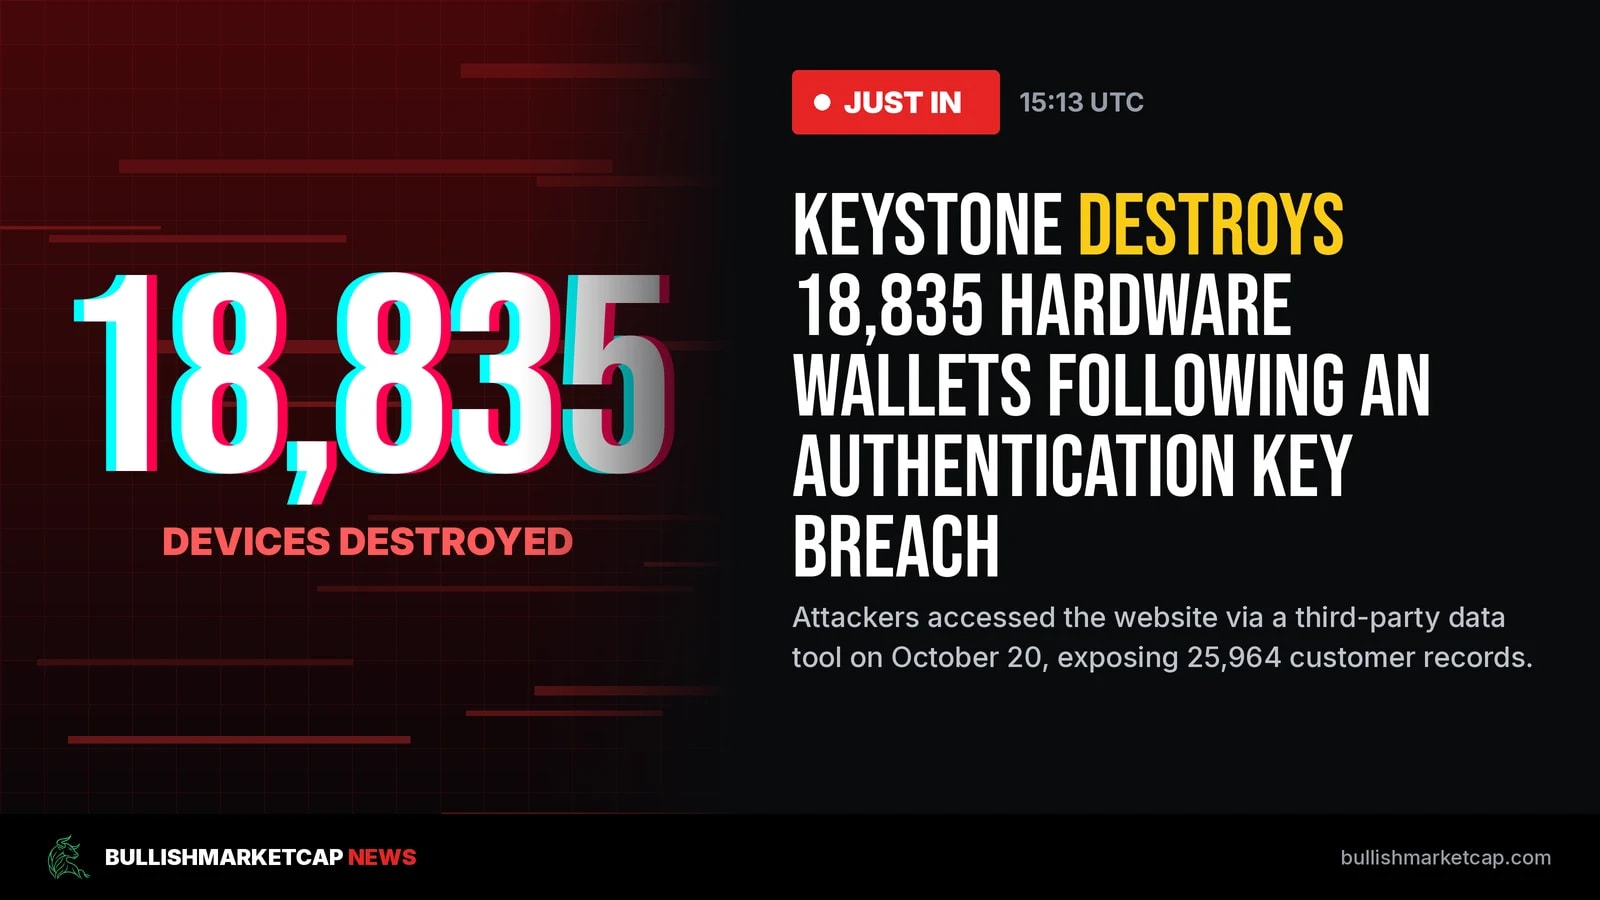
Hardware wallet manufacturer Keystone confirmed that hackers stole a device authentication key and exposed personal information belonging to 25,964 customers, forcing the company to destroy 18,835 inventory units and suspend unfulfilled shipments, according to CryptoNews.
According to the company's security announcement, attackers gained unauthorized access to its official website on October 20 by exploiting a vulnerability in a third-party data monitoring tool. The breach exposed customer names, contact details, shipping addresses, and order details from purchases made between 2024 and 2026. Keystone stated that recovery phrases, private keys, wallet credentials, banking information, and government identification numbers were not compromised.
Instant Telegram notifications for large on-chain moves.
Device Destruction and Shipments
The stolen credential, known as the WebAuth key, is embedded during manufacturing and used when customers verify their devices on the company website. While the key cannot be erased or rewritten, its exposure creates a verification risk because attackers could potentially manufacture counterfeit devices capable of passing official authenticity checks.
As a precaution, Keystone stopped using the compromised key and decided to destroy 18,835 hardware wallets currently in inventory containing the old key. Production has shifted to a replacement authentication key, and shipments of unfulfilled website orders remain on hold while sales continue through a preorder model.
Data Retention Policy Changes
Keystone's investigation revealed that automated deletion tools had failed to remove customer records within the required 180-day period. Following the incident, the company shortened its data retention window to 90 days and submitted deletion requests to Shopify on October 24 for overdue purchase records and incomplete checkouts.
Affected customers will receive individual email notifications, and the company has submitted regulatory and law enforcement reports in the European Union, United Kingdom, and other jurisdictions.
Key facts
- Hackers stole a device authentication key and exposed personal information belonging to 25,964 customers on October 20.
- Keystone will destroy 18,835 hardware wallets from existing inventory containing the compromised key.
- Recovery phrases, private keys, and wallet credentials were confirmed safe and uncompromised.
- The company shortened its customer data retention period from 180 days to 90 days following the breach.
Source: crypto.news
This article is for information only and is not investment advice. BullishMarketCap news is produced with AI assistance from public sources and reviewed by our editors; see our editorial policy. Spotted an error? Tell us.