Cursor Links Extension Attack to Exposed Credentials
Cursor has urged affected teams to check their machines and rotate exposed credentials after up to 5,000 users potentially received a tampered Claude Code extension.
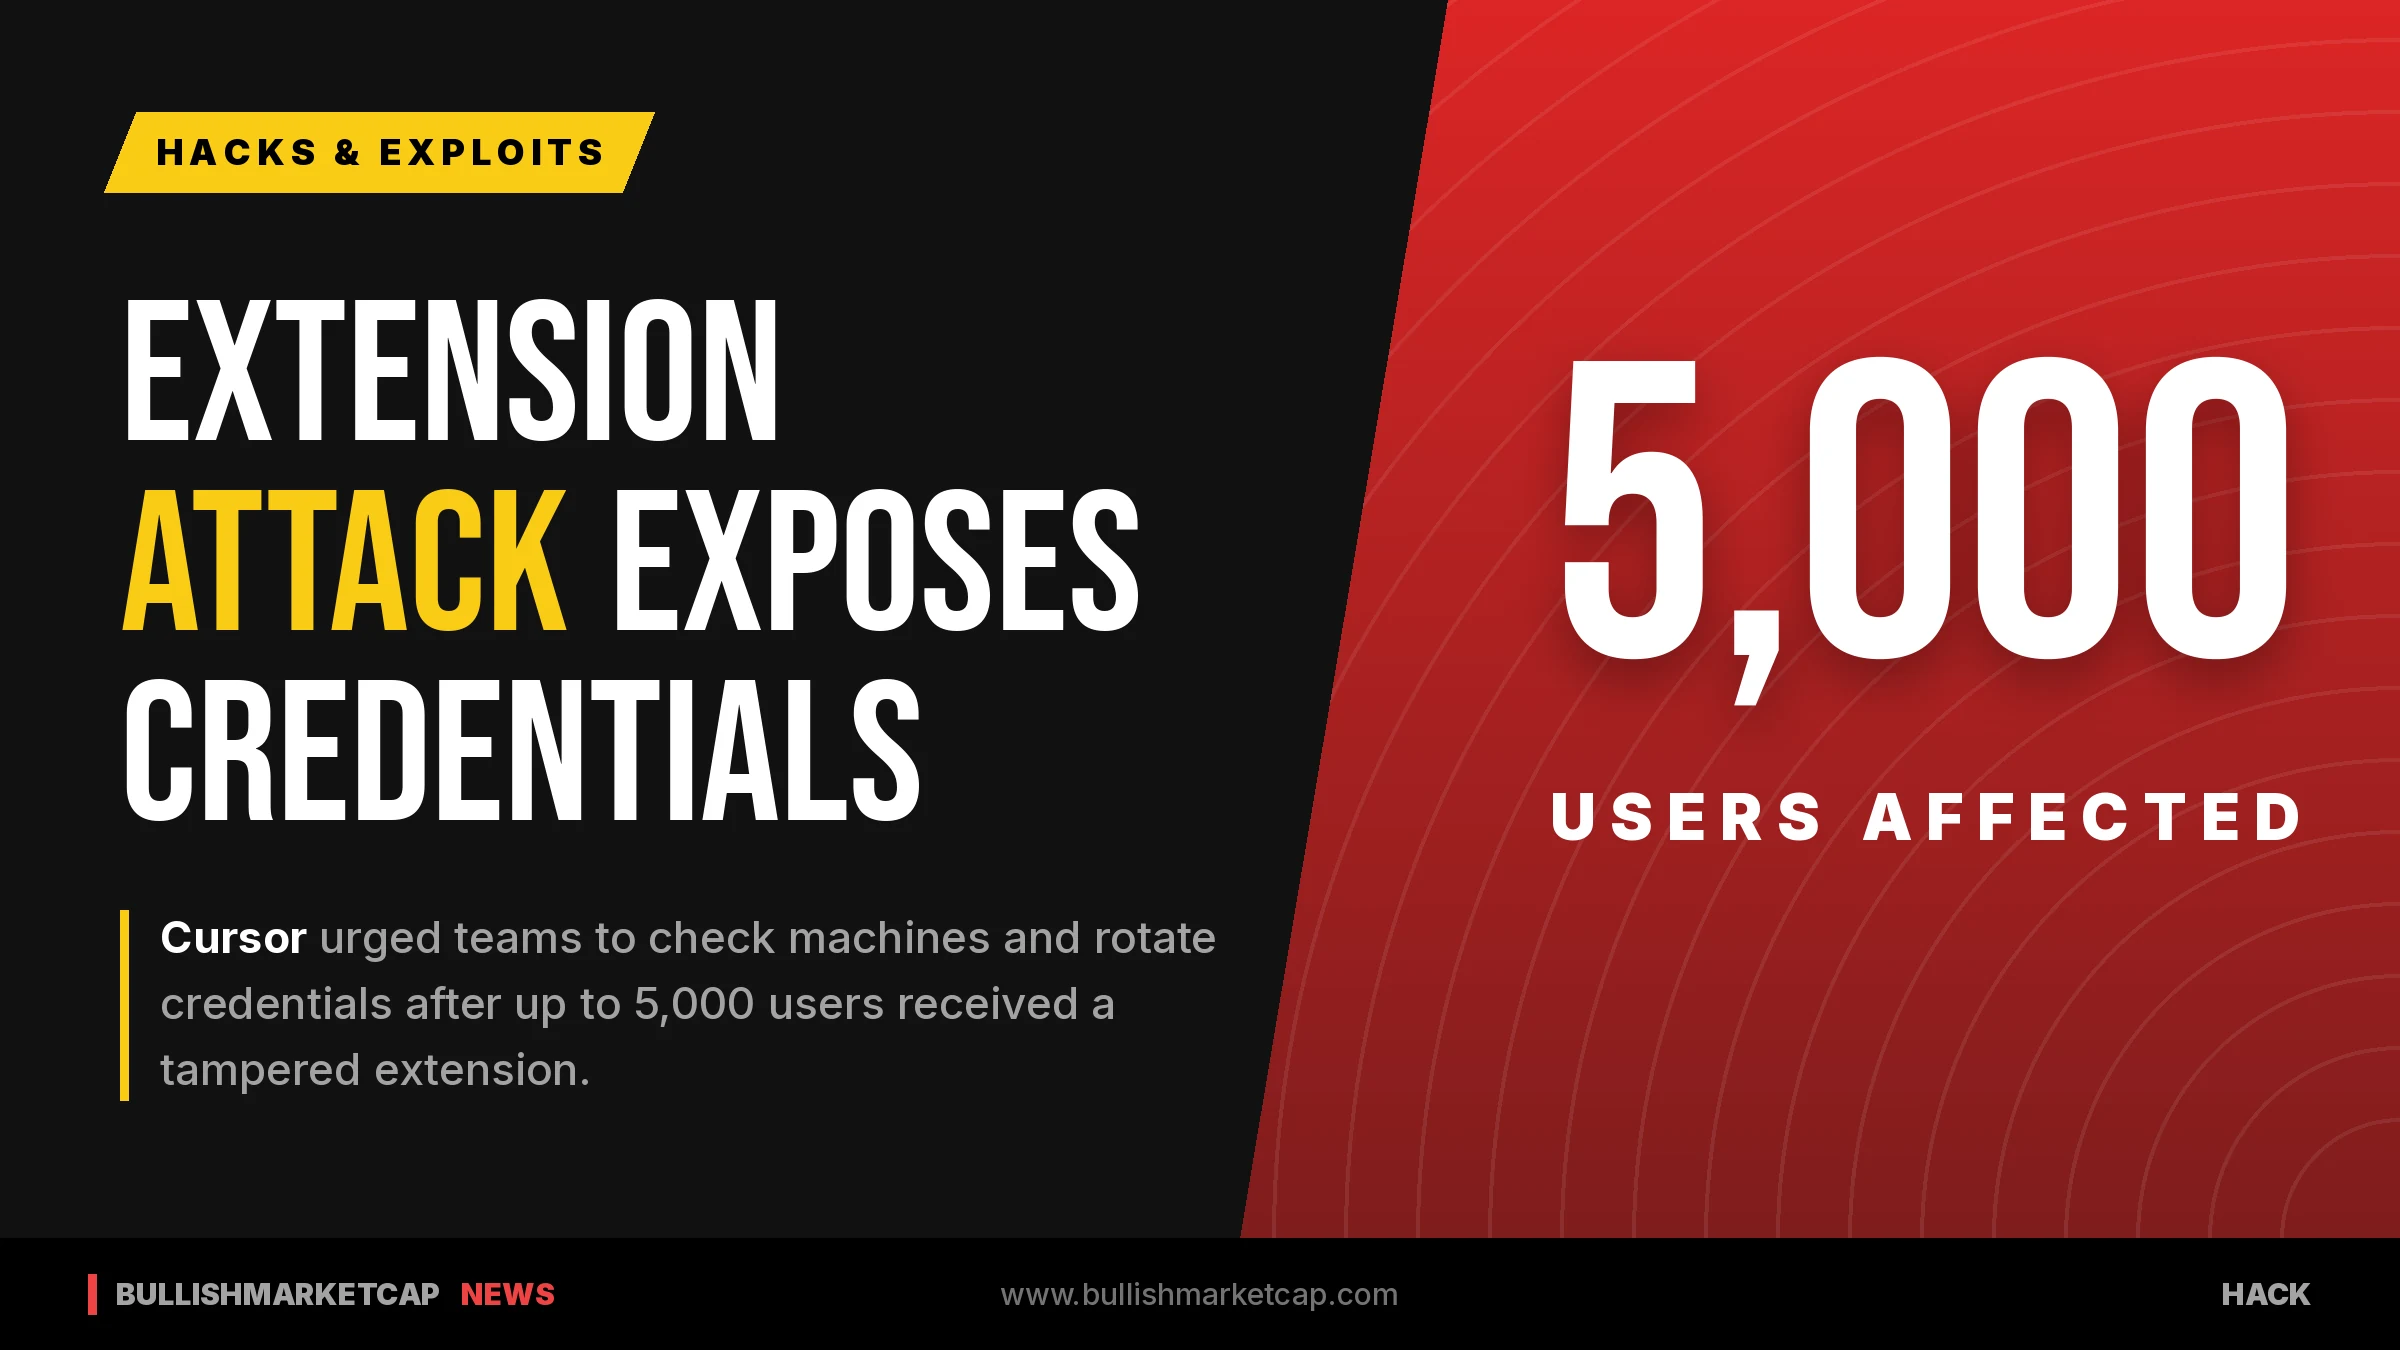
Cursor has linked a recent security attack to exposed credentials, warning that up to 5,000 users potentially received a tampered Claude Code extension, according to TheDefiant.
Security Response
Instant Telegram notifications for large on-chain moves.
Following the incident, Cursor is urging all affected teams to inspect their local machines and immediately rotate any exposed credentials to prevent potential unauthorized access.
Key facts
- Cursor linked the extension compromise to exposed credentials.
- Up to 5,000 users potentially received a tampered Claude Code extension.
- Cursor advised impacted teams to check their systems and rotate exposed credentials.
Source: thedefiant.io
This article is for information only and is not investment advice. BullishMarketCap news is produced with AI assistance from public sources and reviewed by our editors; see our editorial policy. Spotted an error? Tell us.